Hotel Wi-Fi Malware Is Targeting Travelers

The hotel lobby is quiet, your flight landed late, and the only thing standing between you and a warm bed is one final email. You connect your laptop to the guest network, accept the familiar-looking Wi-Fi page, and wait for the browser to load. Instead, a polished notification claims that your browser, network driver, or […]
Malvertising Malware Turns Browsers Into Builders

The creepiest thing about malvertising malware in 2026 is that it no longer has to arrive like a suspicious file waiting in a download folder. It can show up as a clean-looking ad, a fake trading page, or a polished crypto-themed landing screen that feels familiar enough to lower a user’s guard. The victim thinks […]
ViPNet APT Attack Puts Russia on Cyber Alert

The ViPNet APT attack has turned a trusted security tool into the center of a bigger cybersecurity wake-up call, and the timing could not feel more uncomfortable for organizations that depend on private networking software to keep sensitive systems protected. What makes this case stand out is not just that Russian government-linked and regulated organizations […]
ClickLock Stealer Threatens macOS Passwords

The rise of ClickLock Stealer is a sharp reminder that macOS security is no longer a quiet background feature users can simply trust and forget. For years, Mac owners were told, directly or indirectly, that their machines lived slightly outside the messier malware economy surrounding Windows systems. That comfort is now aging badly, because modern […]
North Korean npm Attack Targets Developer Secrets

A routine package installation can look harmless right up until a developer’s credentials, source code, and cloud access keys begin traveling to an attacker-controlled server. That uncomfortable reality sits at the center of the latest North Korean npm attack, a software supply chain campaign designed to turn ordinary development habits into an entry point for […]
ClickFix Malware Evolves With API Delivery

ClickFix malware is no longer just a weird fake CAPTCHA trick hiding on sketchy corners of the web. It has grown into a sharper, more organized delivery system where malicious commands can be served through API-driven infrastructure, making each victim see a slightly different version of the same trap. The scam still leans on a […]
SocGholish Botnet Takedown Hits Evil Corp
The SocGholish botnet has spent years hiding in plain sight, slipping through legitimate websites and turning fake browser updates into a doorway for bigger cyberattacks. Now, a global police operation has punched a serious hole through that infrastructure, disrupting servers, domains, and thousands of compromised websites tied to the malware pipeline. The move matters because […]
WhatsApp Spyware Attack Raises New Alarms
The latest WhatsApp spyware attack story reads less like a routine cybersecurity update and more like a warning flare for the entire digital world. A messaging app used for family chats, newsroom coordination, business calls, activist networks, school groups, and political conversations has once again found itself in the crosshairs of commercial spyware. This time, […]
Gamaredon WinRAR Exploit Threatens Ukraine
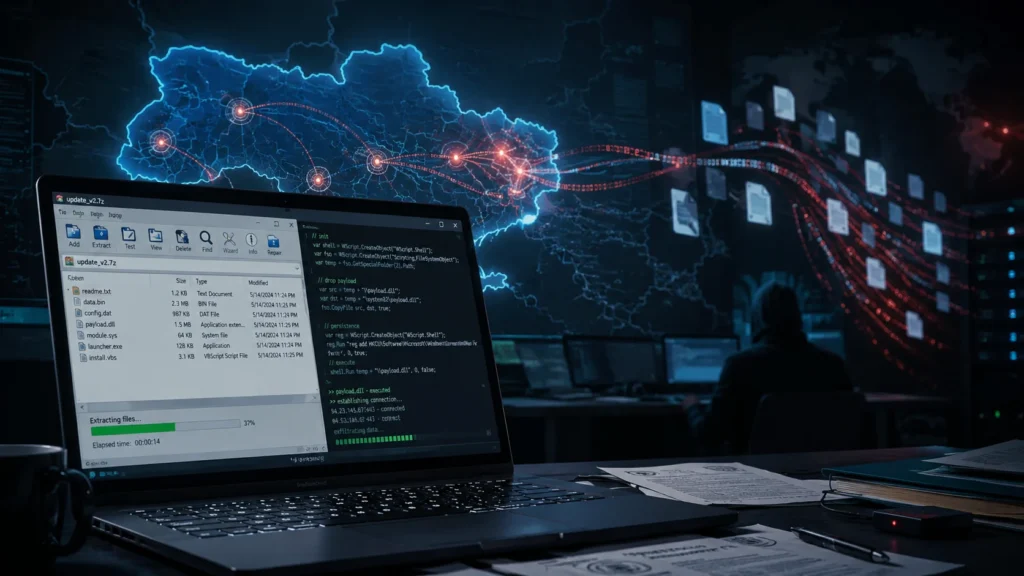
The Gamaredon WinRAR exploit story feels like another reminder that modern cyberwar does not always begin with a dramatic breach screen or a flashy ransomware note. Sometimes, it begins with a familiar archive file, a routine click, and a tool millions of Windows users have treated as harmless for years. In Ukraine’s ongoing digital battlefield, […]
Red Hat NPM Supply Chain Attack Raises Alarm
The Red Hat NPM supply chain attack landed like one of those security stories that feels technical at first, then suddenly becomes everyone’s problem. What started as a compromise involving official-looking packages under the Red Hat Cloud Services npm namespace quickly turned into a bigger warning about how fragile modern software pipelines can be. Developers […]